
WethosAI for Cybersecurity
Attackers study your people. Do you?
WethosAI models the people, authority and operating context involved in a security control or crisis, then runs the scenario repeatedly to expose recurring failures and test the fix.
Model the people
Apply pressure
Reveal the failure pattern
Test the fix
Example: an executive impersonation
Does your help desk still verify identity when someone claims to be an executive?
1 · The request
Someone claims to be an executive and urgently asks the help desk to reset their MFA.
2 · 50 runs
WethosAI runs the scenario 50 times. In this illustrative example, the help desk skips identity verification 18 times.
3 · The change, tested
The team adds out-of-band verification: confirming the request through a separate, known contact. In another 50 runs, verification is skipped 3 times.
Mapped to MITRE ATT&CK®
- ATT&CK techniqueImpersonation
- Targeted personHelp desk agent
- DecisionApprove or reject the MFA reset
- ControlIdentity verification
Illustrative simulation. These results are fictional — not customer outcomes or predictions.
Current procedure
18
of 50 runs skipped identity verification
With out-of-band verification
3
of 50 runs skipped identity verification
83%
fewer skipped verifications
What this gives your team: find where a response process breaks under pressure, change the procedure, and test it again before a real incident.
T1684.001 Social Engineering: Impersonation · Help desk MFA reset. Mapped to MITRE ATT&CK v19.2, released 6 August 2026. WethosAI is not affiliated with or endorsed by The MITRE Corporation.
MITRE ATT&CK® and ATT&CK® are registered trademarks of The MITRE Corporation. Use of MITRE ATT&CK does not imply endorsement or support of WethosAI by MITRE.
Cybersecurity Applications
One platform. Two ways to apply it in cybersecurity.
Start with one critical approval, or rehearse an incident across the organization.
01
Validate a human control
Test one consequential decision repeatedly under changing pressure to find where verification, approval or escalation breaks down.
Best for
- Identity and MFA resets
- Treasury wires and vendor bank changes
- Privileged-access and AI-agent approvals
02
Rehearse a cyber crisis
Simulate an incident end to end across the people, roles, authority and escalation paths involved.
Best for
- Ransomware and data breaches
- C-suite and board exercises
- Insider, third-party and AI-agent incidents
Who built it
Built by a cybersecurity pioneer.
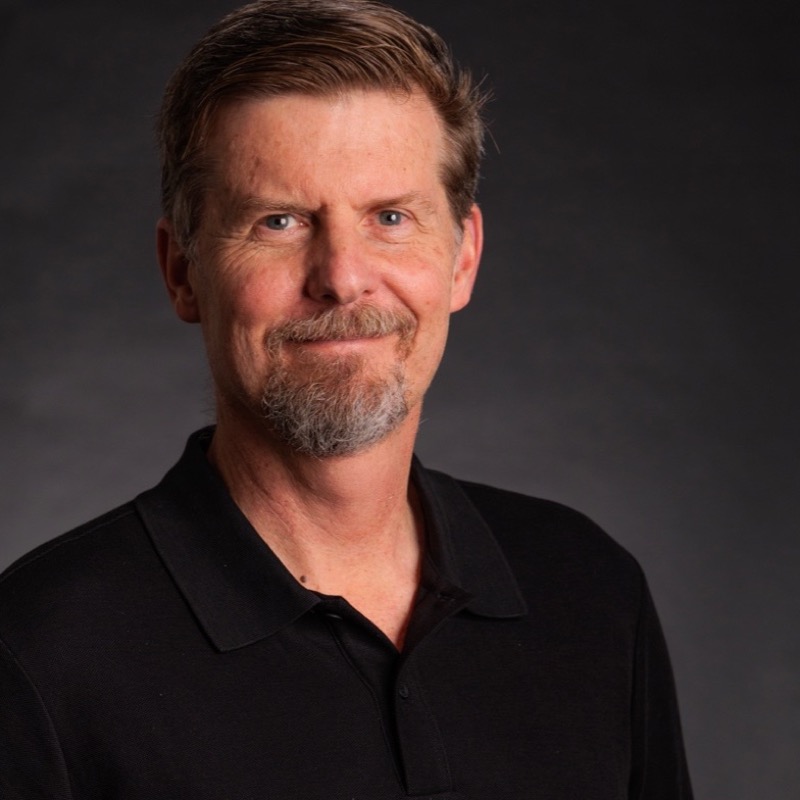
Stuart McClure founded Foundstone, served as global CTO of McAfee and co-founded Cylance, acquired by BlackBerry for $1.4 billion. His experience shapes how WethosAI tests the human decisions that critical controls and crisis plans depend on.
Why now
AI is increasing the pressure on human controls.
- Attackers use AI to create faster, more personalized impersonation attempts.
- AI agents can request access, recommend payments and initiate operational actions.
- Existing controls rarely test how people and AI agents behave together under pressure.
How It Works
Model. Simulate. Find the pattern. Test the fix.
01
Model the people
Represent the employees, leaders and attackers who can change the outcome.
02
Add operating context
Include controls, policies, authority, escalation paths and business constraints.
03
Run repeated simulations
Vary urgency, evidence, authority and attacker tactics to expose recurring failures.
04
Change and rerun
Test a revised control and measure whether the outcome improves.
What the simulation surfaces
- Recurring failure patterns
- Authority and escalation breakdowns
- Control-change recommendations
- Before-and-after rerun results
Who Participates
Model the people and expertise that shape the outcome.
Simulations combine specific Modeled Stakeholders, permission-based Twins and purpose-built Expert Agents, including attackers, regulators and incident-response experts.
Models surface probabilistic patterns and pressure points. They do not diagnose people, predict behavior with certainty or act with anyone’s authority.
Trust
Built for enterprise security requirements.
SOC 2 Type II
Independent attestation
SSO
Access follows your directory, including removal
Role-based access controls
Who runs, views, exports
No customer data used to train shared models
Research
Research informing our approach.
New from Stuart McClure
Human + AI Alignment
Stuart McClure explains why reliable AI oversight depends on the people, authority and operating conditions surrounding the system.
- Human-Centered CybersecurityNIST · Updated 14 September 2026
- What Comes After Behavior Change?SANS · Lance Spitzner · 9 September 2026
- A Decade of GHOSTS in the MachineCarnegie Mellon SEI · 10 August 2026
Independent research informing the field. Links do not imply endorsement.
Test the human decisions your security depends on.
Bring us one critical control or crisis scenario. We’ll show you how WethosAI models it, runs it repeatedly and tests the fix.